01
Step 1 of 5
Discover
See every AI agent, identity, data flow and exposure in scope, with each module writing to the same record.
Explore AI Identity & Trust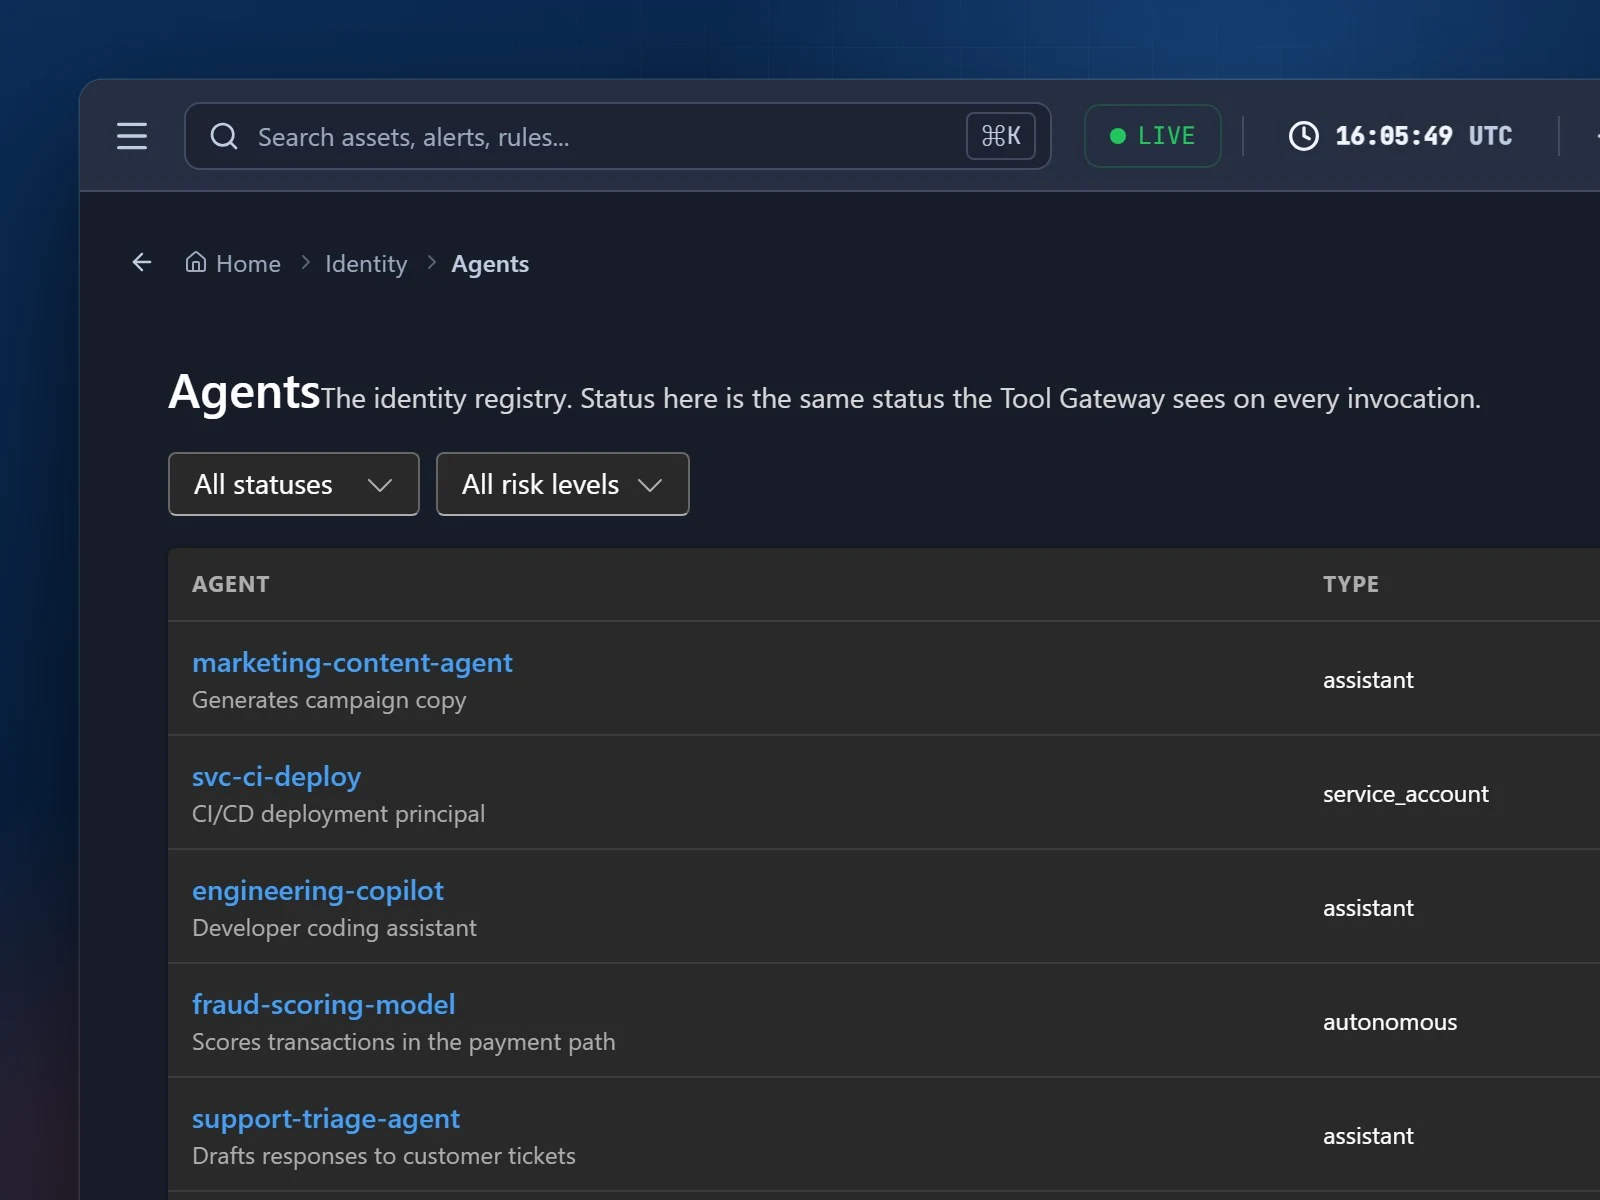
Home ARGUS ONE
A 360CyberX product
Every AI agent, assistant and model in your organisation gets an identity. ARGUS ONE records what each one does and turns that activity into risk, investigations and response, working alongside the security tools you already run.
Why it matters
An attacker can move from a phishing email to an AI agent's credentials to a sensitive dataset in minutes. The evidence ends up spread across identity, email, data and compliance tools, owned by different teams, and nobody holds one record of what the agent did.
Identity, email, data and compliance tools each see one slice of what an AI agent did. None of them shows the whole route an attack took.
AI agents hold credentials and reach tools and data, yet they sit outside what SIEM, EDR and cloud security tools were built to watch.
Investigations, board reports and audit evidence are pieced together from exports every time someone asks for them.
How it works
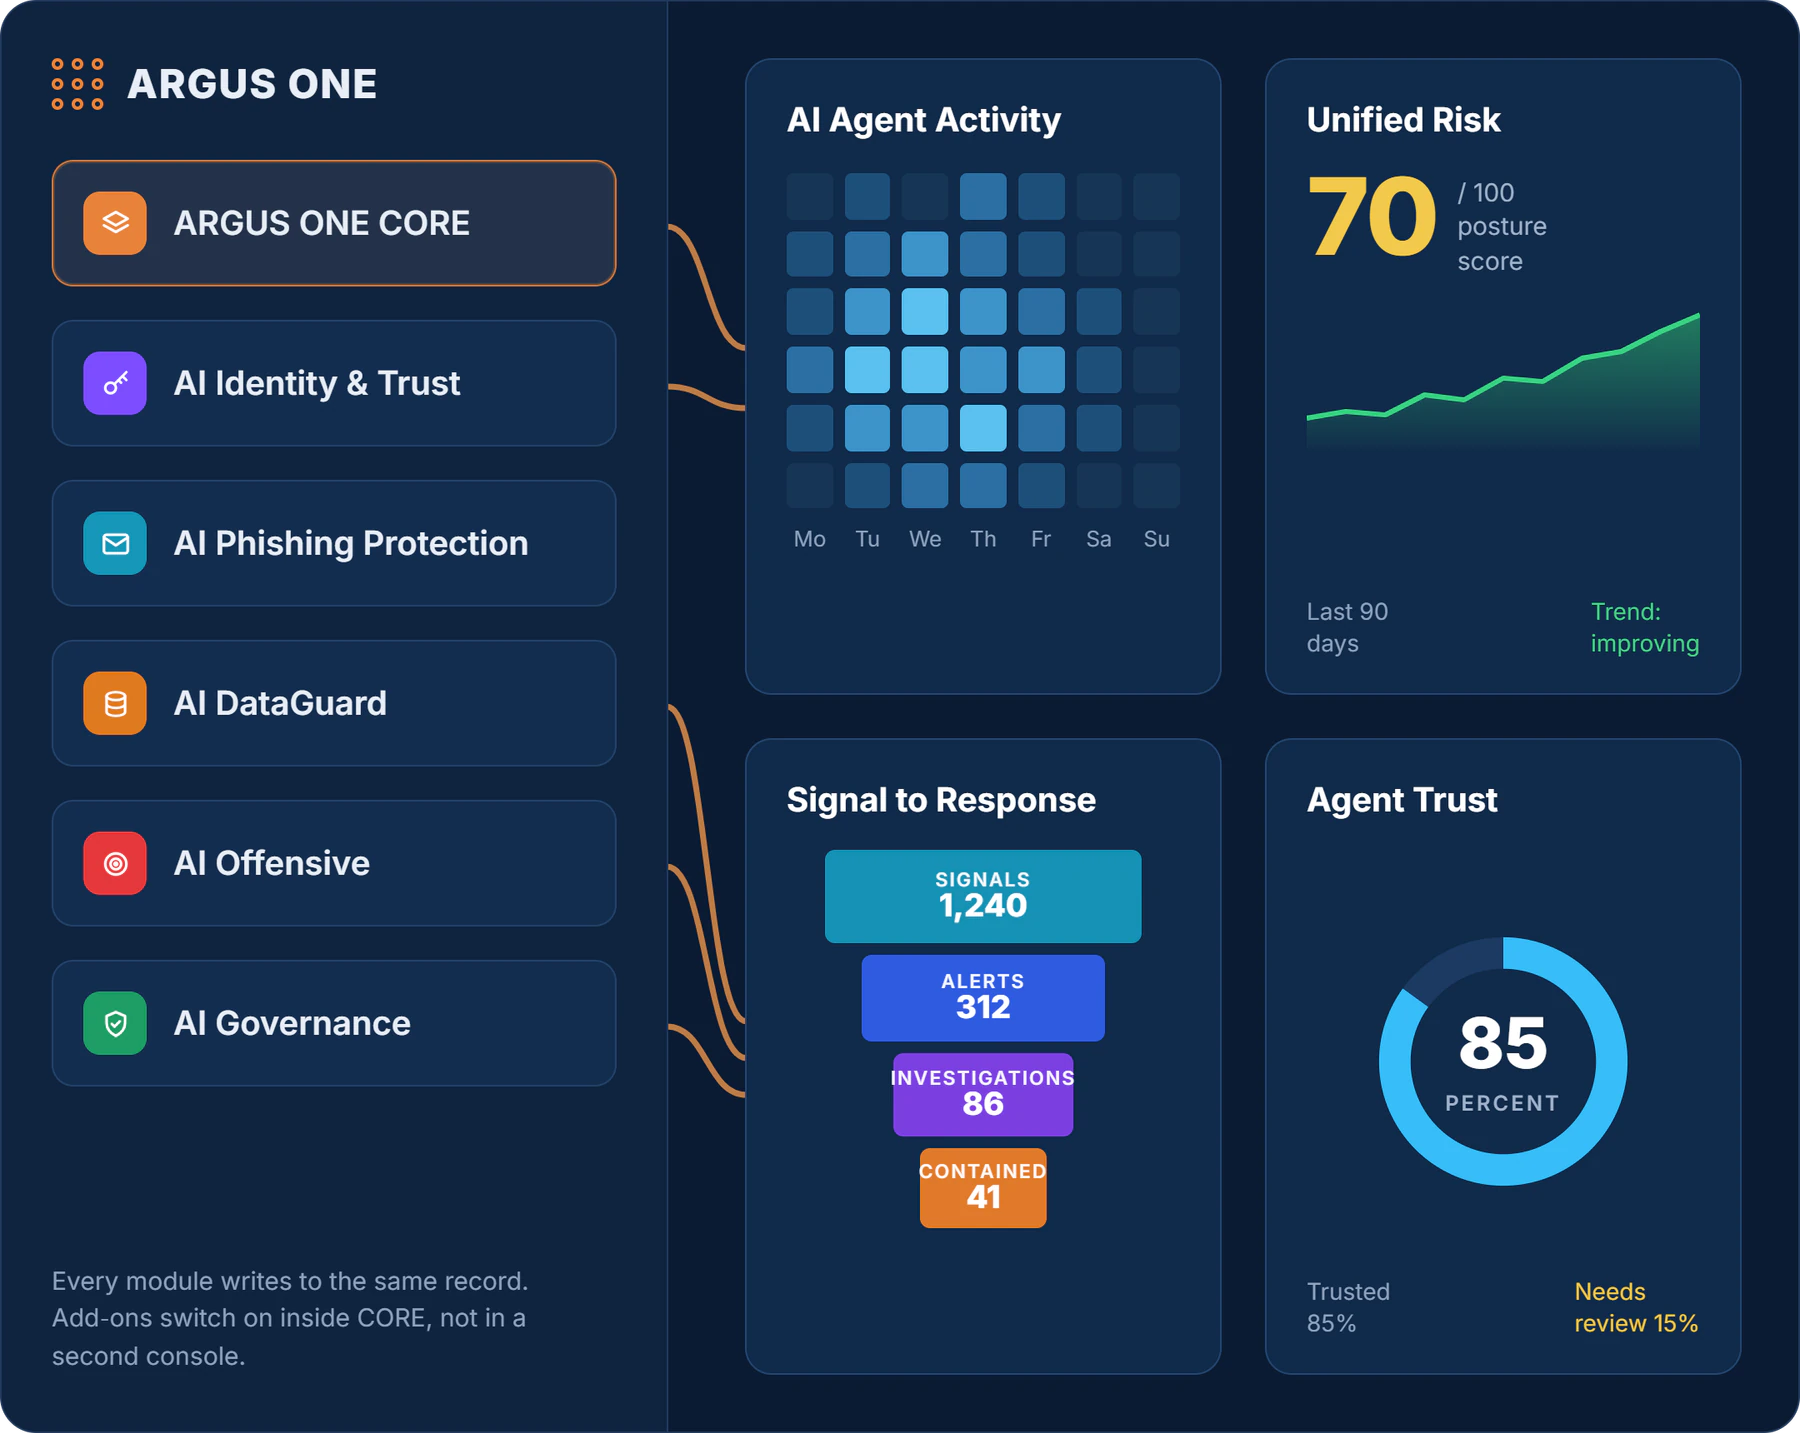
Everything lands in one findings model with identity, asset and data context, so your team works one case instead of three tickets. Each slide shows the step in ARGUS ONE.

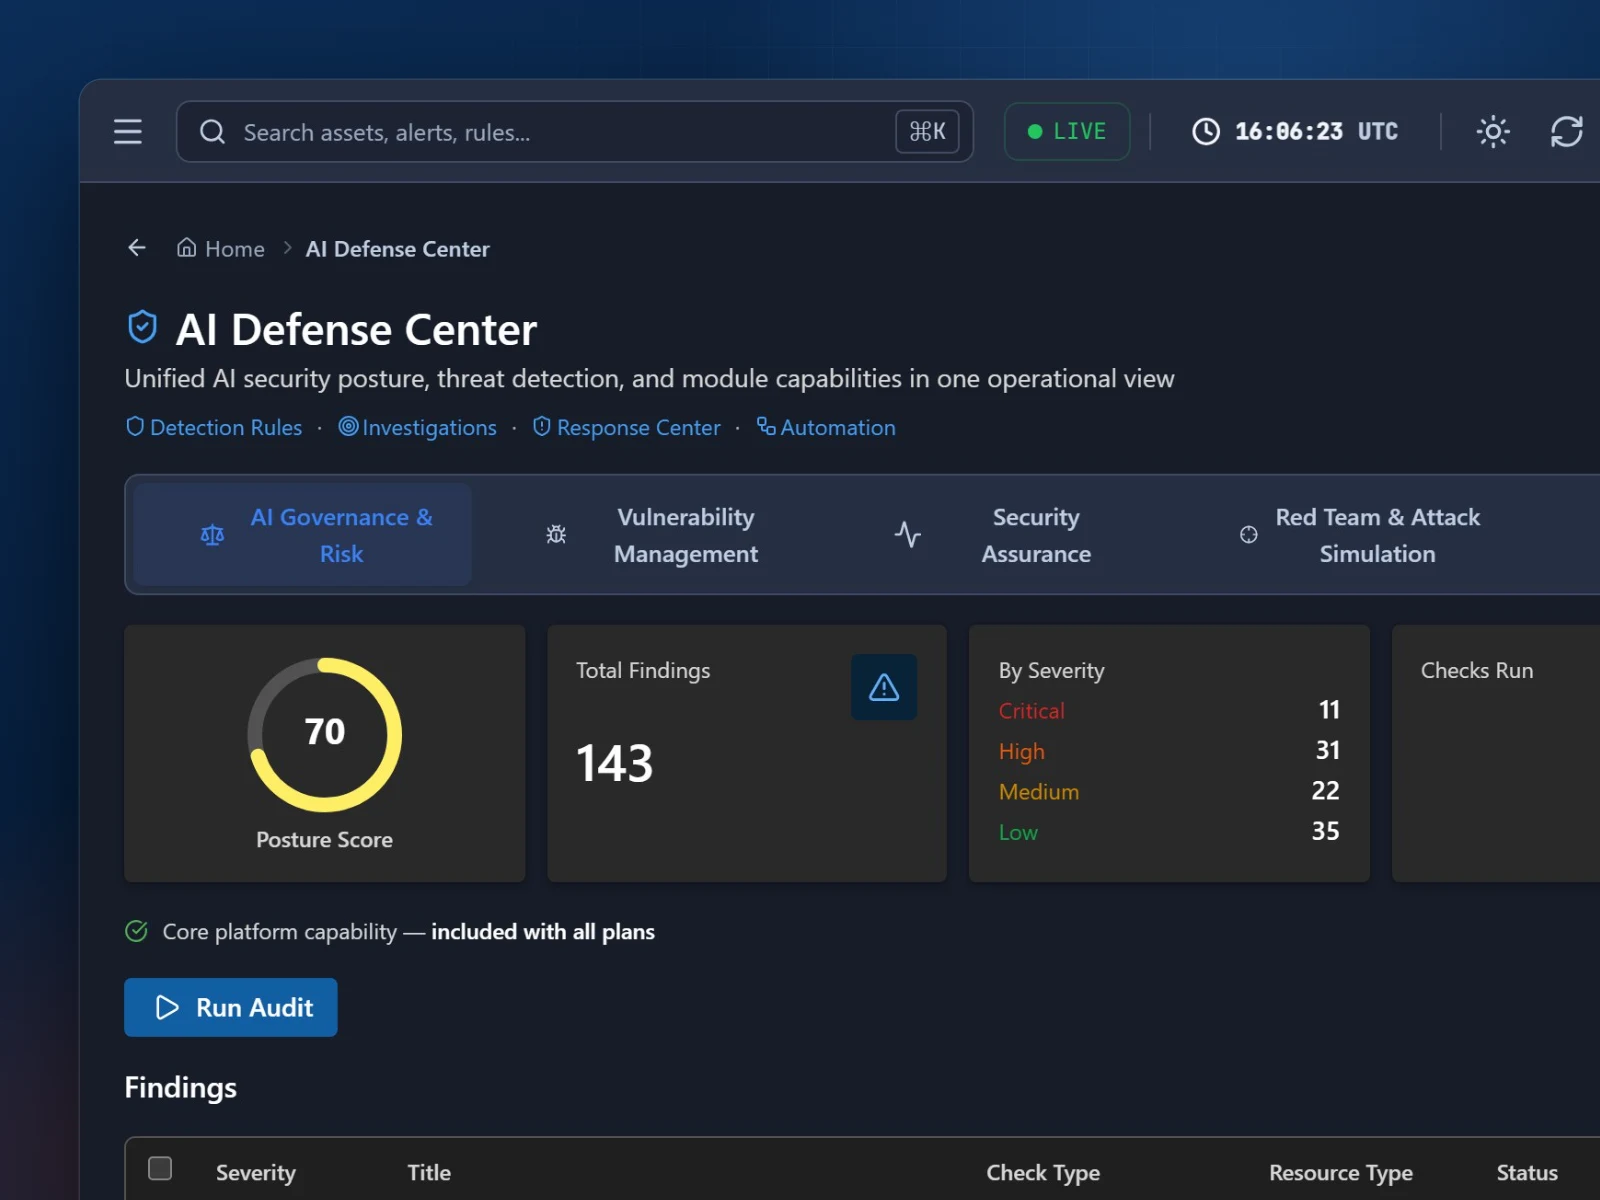
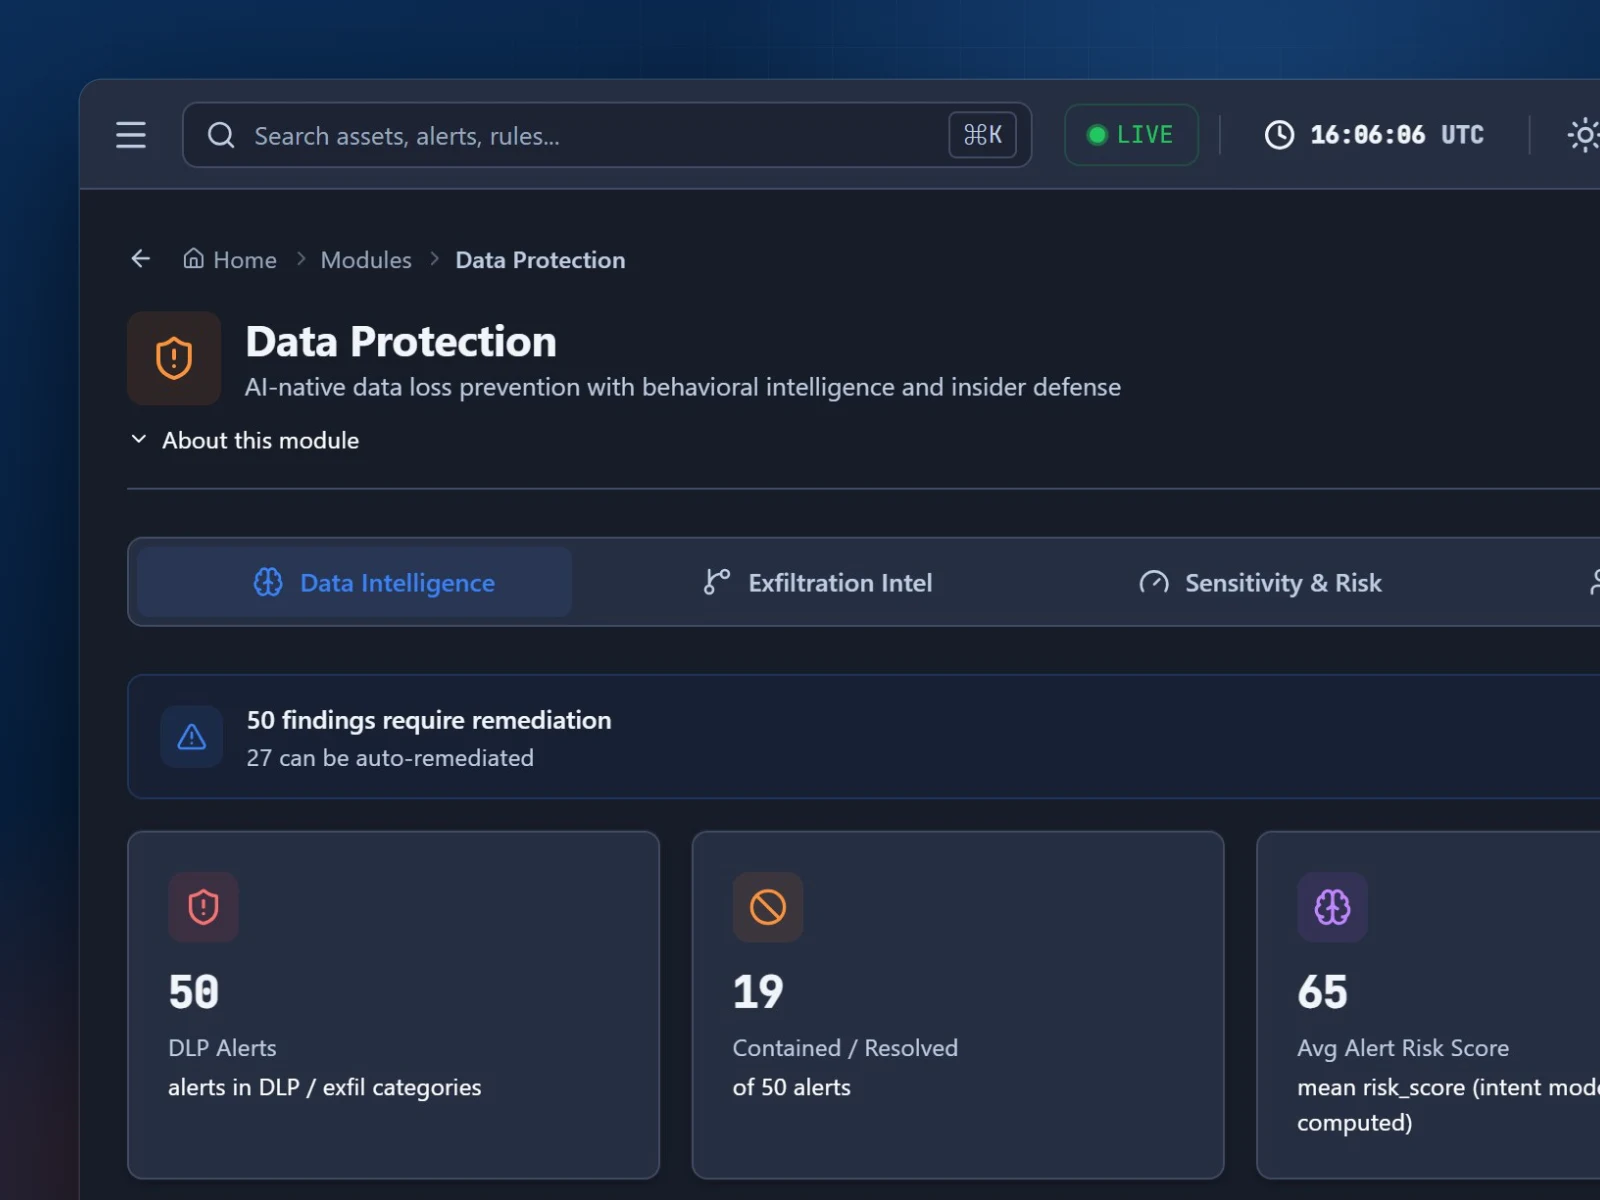
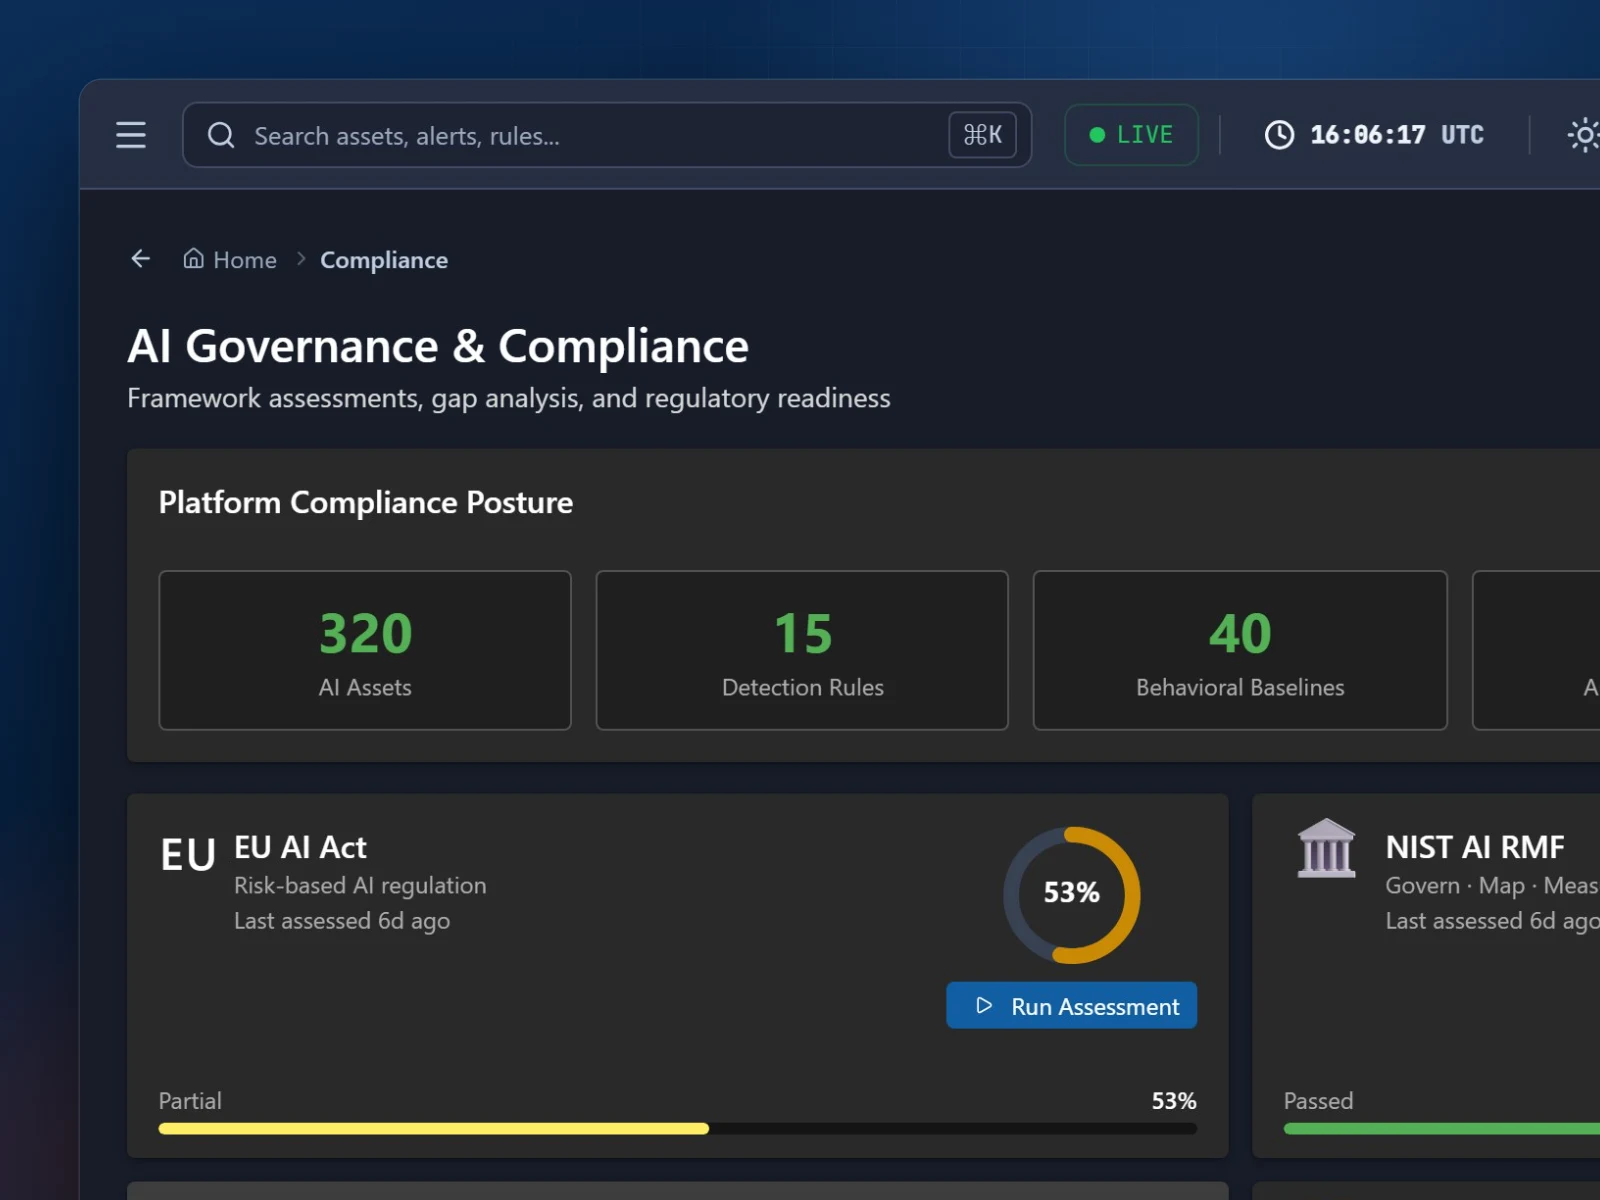
Product images show a demonstration environment.
Use cases
 SOC leaderAccount and credential takeoverOne investigation instead of three tickets, and containment before the export completes.Read the use case
 CISOPhishing and business email compromiseConsistent phishing decisions with an evidence trail and a measurable picture of human risk.Read the use case
 Security engineerSensitive data exposure in AI workflowsExposures caught with the path they took, and proof that your controls worked.Read the use case
 Security engineerAttack-path discoveryRemediation effort spent on the paths an attacker could actually use.Read the use case
 Procurement and GRCCompliance readiness for AI systemsAudit readiness as a result of daily operations instead of a quarterly project.Read the use case
 CISOAI agent identity riskAgent identities that are owned, scoped, scored and revocable.Read the use case
Modules
ARGUS ONE CORE is the foundation of every deployment. Add any of the five modules on its own. They all share one findings model, one risk engine and one investigation workspace, so each module makes the others more useful, and nothing is repackaged or migrated when you add one.
Integrations
ARGUS ONE adds to your security stack instead of replacing it. Findings and actions flow through these integrations, and high-risk actions wait for a person to approve them.
These ship today. More are planned, and the ARGUS ONE platform page lists each one with its status.
How to buy
Every quote is scoped to your environment. There are no published list prices.
Every deployment starts here: registry, telemetry, detection, investigations, Response Center, automation, Copilot and audit.
Add any of the five modules on its own, each switching on inside the same platform.
CORE with all five modules, for organisations that want the full intelligence layer.
Terms agreed with you for larger programmes and specific contract needs.
Customers can trial any add-on module for 90 days from inside the platform.
Questions
More answers on packaging, deployment, AI and data handling are in the ARGUS ONE FAQ and on its security and trust page.
No. It works alongside the security tools you already run and sends findings and actions through integrations such as Splunk, Microsoft Sentinel, ServiceNow and Microsoft Teams.
No. Every deployment starts with ARGUS ONE CORE, and you add modules one at a time when your programme needs them.
Yes. Customers can trial any add-on module for 90 days from inside the platform.
Your team does. Playbooks act through your integrations, and high-risk actions wait for a person to approve them. Every recommendation from Argus Copilot is logged in your tenant.
360CyberX, the Dallas cybersecurity and IT firm behind this website. ARGUS ONE runs on its own platform at argus.360cyberx.com, with its own sign in and security controls.
Get started
A product specialist walks you through the platform using the AI agents, assistants and data flows you bring, not a slide deck.
Demo requests, pricing and sign in continue on argus.360cyberx.com, the ARGUS ONE site run by 360CyberX.